
Configuring signal thresholds (site alerts)
- English
- 日本語
Signal thresholds (also known as site alerts) are a type of threshold configuration that you can create to monitor and handle requests from IP addresses that contain specific signals. A signal threshold (site alert) outlines:
- the criteria that must be met for an IP address to be flagged. For example, flag an IP address when there are 25 SQL Injection attack signals in 1 minute.
- how to handle requests from IP addresses that are flagged. You can either log subsequent requests or block subsequent requests containing attack signals from the IP address.
- how long to block or log subsequent requests from flagged IP addresses.
Limitations and considerations
When working with signal thresholds (site alerts), keep the following things in mind:
- Accounts are limited to 50 signal thresholds (site alerts) per workspace (site).
- Signal thresholds (site alerts) are considered custom rules for purposes of packaged entitlement limitations.
- If you've been assigned an observer role (or the user or billing role), you cannot configure signal thresholds (site alerts).
- You can block all requests from IP addresses that have been flagged for events using request rules with the Site Flagged IP (
SITE-FLAGGED-IP) anomaly signal. However, it is not included with the Essential or Professional platforms.
Adding signal thresholds (site alerts)
To create a signal threshold (site alert), follow the instructions for the control panel that you use to access the Next-Gen WAF.
- Fastly control panel
- Next-Gen WAF control panel
- Log in to the Fastly control panel.
- Go to Security > Next-Gen WAF > Signals.
- From the workspaces bar, click the menu
 to the right of the workspace name and select a workspace.
Click the document icon
 next to the appropriate signal.
Click Add signal threshold.

Fill out the Add signal threshold form as follows:
- In the Name field, enter a descriptive name for the signal threshold.
- In the Threshold field, enter how many requests containing the signal should be detected before the IP address is flagged.
- From the Interval menu, select the number of minutes during which signals from the IP address are counted to determine if the threshold has been met.
- Under When an IP hits the threshold, select whether the threshold should log a sample of subsequent requests from the IP address or block subsequent requests containing attack signals from the IP address. If you selected an anomaly signal from the Signal menu, then you will only be able to log subsequent requests from the IP address. If you're on the Essential platform and selected a CVE signal from the Signal menu, you can only block subsequent requests.
- From the Duration menu, select how long the IP address should be flagged. By default, IP addresses are flagged for 24 hours. You can set a custom duration by selecting Custom and then setting a duration.
- Leave the Notifications checkbox selected to send an external notification (e.g., email and Slack) when the signal threshold is triggered. Deselect the checkbox to not send any external notifications.
- Click the Status switch to enable the signal threshold.
Click Add signal threshold.
The steps to add a site alert depend on the platform or packaged offering that you've purchased.
- For the Professional and Premier platforms or a packaged offering, use the Site Alerts page.
- For the Essential platform, use the Signals page.
Site Alerts page
If you're on the Professional or Premier platform or have purchased the Security Core, Security Core Plus, or Security Total packaged offering, complete the following steps:
- Log in to the Next-Gen WAF control panel.
- From the Sites menu, select a site if you have more than one site.
From the Rules menu, select Site Alerts.
Click Add site alert.
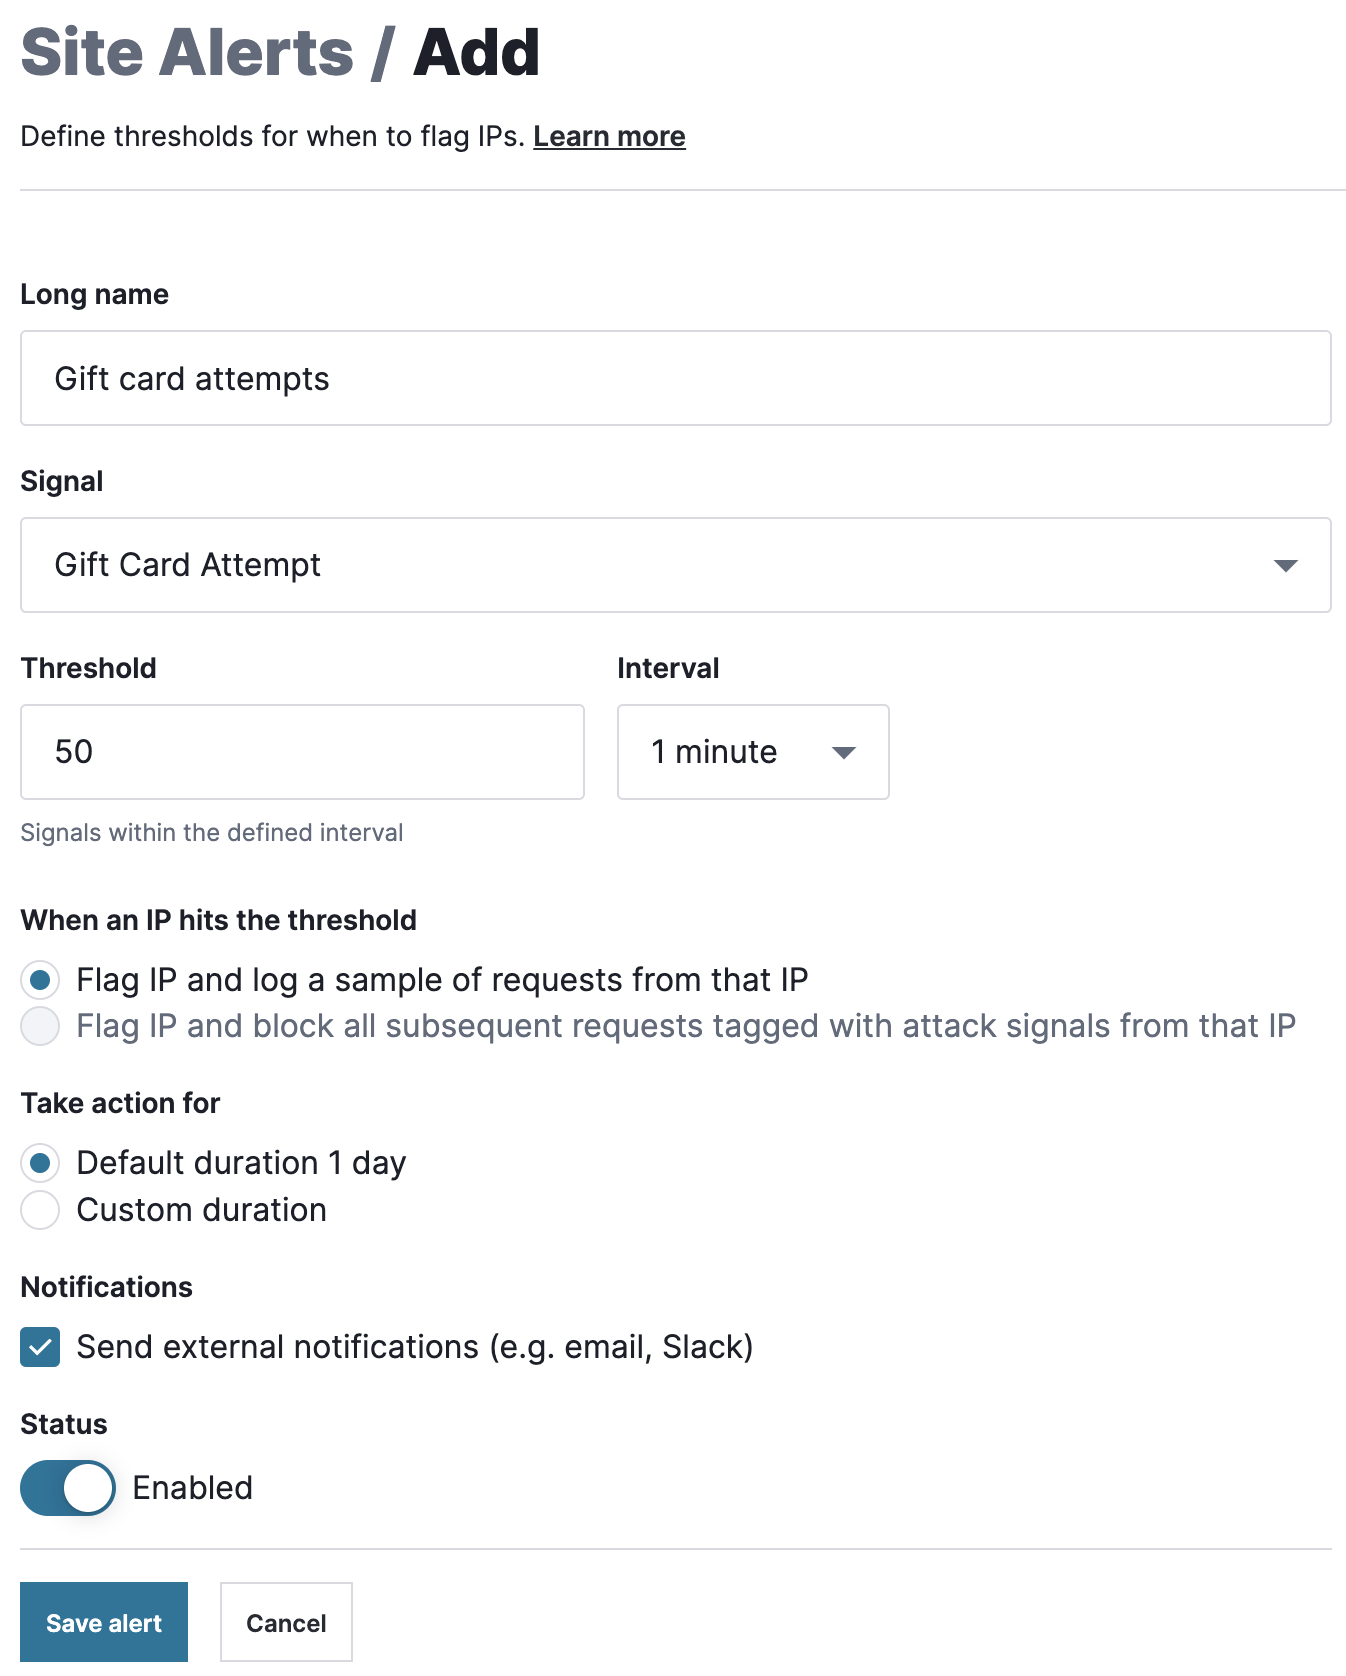
Fill out the Add form as follows:
- In the Long name field, enter a descriptive name for the alert.
- From the Signal menu, select the signal that the site alert should track.
- In the Threshold field, enter how many requests containing the signal should be detected before the IP address is flagged.
- From the Interval menu, select the number of minutes during which signals from the IP address are counted to determine if the threshold has been met.
- Under When an IP hits the threshold, select whether the alert should log a sample of subsequent requests from the IP address or block subsequent requests containing attack signals from the IP address. If you selected an anomaly signal from the Signal menu, then you will only be able to log subsequent requests from the IP address.
- Under Take action for, select how long the IP address should be flagged. By default, IP addresses are flagged for 24 hours. You can set a custom duration by selecting Custom duration and choosing a duration.
- Leave the Notifications checkbox selected to send an external notification (e.g., email and Slack) when the site alert is triggered. Deselect the checkbox to not send any external notifications.
- Click the Status switch to enable the site alert.
Click Save alert.
Signals page
If you're on the Essential platform, complete the following steps:
- Log in to the Next-Gen WAF control panel.
- From the Sites menu, select a site if you have more than one site.
Click the Signals tab.
On the Signals page, click View in the row of the CVE signal that you want to enable.
Click the Configuration tab.
Click the Alerts tab and then Add alert.
Fill out the alert fields as follows:
- In the Long name field, enter a descriptive name for the alert.
- In the Threshold field, enter how many requests containing the signal should be detected before the IP address is flagged.
- From the Interval menu, select the number of minutes during which signals from the IP address are counted to determine if the threshold has been met.
- Under When an IP hits the threshold, select whether the alert should log subsequent requests or block subsequent requests containing attack signals from the IP address. For CVE signals, you can only block subsequent requests.
- Under Take action for, select how long the IP address should be flagged. By default, IP addresses are flagged for 24 hours. You can set a custom duration by selecting Custom duration and choosing a duration.
- Leave the Notifications checkbox selected to send an external notification (e.g., email and Slack) when the site alert is triggered. Deselect the checkbox to not send any external notifications.
- Click the Status switch to enable the site alert.
Click Save alert.
Editing signal thresholds (site alerts)
To edit a signal threshold (site alert), follow the instructions for the control panel that you use to access the Next-Gen WAF.
- Fastly control panel
- Next-Gen WAF control panel
- Log in to the Fastly control panel.
- Go to Security > Next-Gen WAF > Signals.
- From the workspaces bar, click the menu to the right of the workspace name and select a workspace.
Click the document icon
next to the appropriate signal.Click the Configuration tab and then the Thresholds tab.
Click the pencil
 to the right of the signal threshold that you want to edit.

Fill out the Edit signal threshold form as follows:
- In the Name field, enter a descriptive name for the signal threshold.
- In the Threshold field, enter how many requests containing the signal should be detected before the IP address is flagged.
- From the Interval menu, select the number of minutes during which signals from the IP address are counted to determine if the threshold has been met.
- Under When an IP hits the threshold, select whether the threshold should log a sample of subsequent requests from the IP address or block subsequent requests containing attack signals from the IP address. If you selected an anomaly signal from the Signal menu, then you will only be able to log subsequent requests from the IP address. If you're on the Essential platform and selected a CVE signal from the Signal menu, you can only block subsequent requests.
- From the Duration menu, select how long the IP address should be flagged. By default, IP addresses are flagged for 24 hours. You can set a custom duration by selecting Custom and then setting a duration.
- Leave the Notifications checkbox selected to send an external notification (e.g., email and Slack) when the signal threshold is triggered. Deselect the checkbox to not send any external notifications.
- Click the Status switch to the On position to enable the signal threshold or the Off position to disable the signal threshold.
Click Update signal threshold.
The steps to edit a site alert depend on the platform or packaged offering that you've purchased.
- For the Professional and Premier platforms or a packaged offering, use the Site Alerts page.
- For the Essential platform, use the Signals page.
Site Alerts page
If you're on the Professional or Premier platform or have purchased the Security Core, Security Core Plus, or Security Total packaged offering, complete the following steps:
- Log in to the Next-Gen WAF control panel.
- From the Sites menu, select a site if you have more than one site.
From the Rules menu, select Site Alerts.
Click the name of the site alert that you want to edit.
Click Edit site alert.
Fill out the Edit form as follows:
- In the Long name field, enter a descriptive name for the alert.
- From the Signal menu, select the signal that the site alert should track.
- In the Threshold field, enter how many requests containing the signal should be detected before the IP address is flagged.
- From the Interval menu, select the number of minutes during which signals from the IP address are counted to determine if the threshold has been met.
- Under When an IP hits the threshold, select whether the alert should log a sample of subsequent requests from the IP address or block subsequent requests containing attack signals from the IP address. If you selected an anomaly signal from the Signal menu, then you will only be able to log subsequent requests from the IP address.
- Under Take action for, select how long the IP address should be flagged. By default, IP addresses are flagged for 24 hours. You can set a custom duration by selecting Custom duration and choosing a duration.
- Leave the Notifications checkbox selected to send an external notification (e.g., email and Slack) when the site alert is triggered. Deselect the checkbox to not send any external notifications.
- Click the Status switch to the On position to enable the site alert or the Off position to disable the site alert.
Click Save alert.
Signals page
If you're on the Essential platform, complete the following steps:
- Log in to the Next-Gen WAF control panel.
- From the Sites menu, select a site if you have more than one site.
Click the Signals tab.
On the Signals page, click View in the row of the CVE signal that you want to enable.
Click the Configuration tab and then the Alerts tab.
Click the name of the site alert that you want to modify.
Click Edit alert.
Fill out the alert fields as follows:
- In the Long name field, enter a descriptive name for the alert.
- In the Threshold field, enter how many requests containing the signal should be detected before the IP address is flagged.
- From the Interval menu, select the number of minutes during which signals from the IP address are counted to determine if the threshold has been met.
- Under When an IP hits the threshold, select whether the alert should log subsequent requests or block subsequent requests containing attack signals from the IP address. For CVE signals, you can only block subsequent requests.
- Under Take action for, select how long the IP address should be flagged. By default, IP addresses are flagged for 24 hours. You can set a custom duration by selecting Custom duration and choosing a duration.
- Leave the Notifications checkbox selected to send an external notification (e.g., email and Slack) when the site alert is triggered. Deselect the checkbox to not send any external notifications.
- Click the Status switch to the On position to enable the site alert or the Off position to disable the site alert.
Click Save alert.
Deleting signal thresholds (site alerts)
To delete a signal threshold (site alert), follow the instructions for the control panel that you use to access the Next-Gen WAF.
- Fastly control panel
- Next-Gen WAF control panel
- Log in to the Fastly control panel.
- Go to Security > Next-Gen WAF > Signals.
- From the workspaces bar, click the menu to the right of the workspace name and select a workspace.
- Click the document icon next to the appropriate signal.
- Click the Configuration tab and then the Thresholds tab.
- Click the trash
 next to the signal threshold that you want to delete and then Delete signal threshold.
The steps to delete a site alert depend on the platform or packaged offering that you've purchased.
- For the Professional and Premier platforms or a packaged offering, use the Site Alerts page.
- For the Essential platform, use the Signals page.
Site Alerts page
If you're on the Professional or Premier or have purchased the Security Core, Security Core Plus, or Security Total packaged offering, complete the following steps:
- Log in to the Next-Gen WAF control panel.
- From the Sites menu, select a site if you have more than one site.
- From the Rules menu, select Site Alerts.
- Click the name of the site alert that you want to delete.
- Click Remove site alert and then Delete.
Signals page
If you're on the Essential platform, complete the following steps:
- Log in to the Next-Gen WAF control panel.
- From the Sites menu, select a site if you have more than one site.
- Click the Signals tab.
- On the Signals page, click View in the row of relevant signal.
- Click Configuration and then Alerts.
- Click the name of the site alert that you want to delete.
- Click Remove alert and then Delete.
