

Obtén todo lo que necesitas de una CDN moderna: desde una escala sin esfuerzo y seguridad integrada hasta control programable y visibilidad total.




Seguridad
Page 1 of 19

Fastly Named a Leader in the 2026 IDC MarketScape for WAAP
Fastly named a Leader in the 2026 IDC MarketScape for WAAP. Learn how Fastly protects web apps and APIs with automated defense and low false positives.
AI Bot Cosplay
In a single day over 6M requests posed as AI bots to probe for .env files, Git metadata, credentials and other private files. Unpack the threat of AI bot cosplay and learn how Fastly's WAF rules can block impostors.
Back to Basics: Insecure Deserialization
Learn what insecure deserialization is, how attackers exploit it, and how to prevent attacks using secure coding best practices and the Fastly Next-Gen WAF.
Fastly Unveils AEDA: Autonomous Edge Security in Gemini Enterprise
Discover Fastly’s Autonomous Edge Defense Agent (AEDA) in Gemini Enterprise, designed to streamline incident response and slash MTTR.

Knowledge Is Power: Control AI Bot Scraping with Fastly Bot Management
Learn how Fastly Bot Management and ContentGuard help you strategically control AI scrapers and protect your cached content in the AI era.

Presentamos AI Runtime Control de Fastly: por qué tu estrategia de IA necesita un plano de control
Descubre AI Runtime Control de Fastly. Obtén visibilidad en tiempo real, gestiona el gasto en tokens y controla de forma segura el uso de la IA empresarial en el edge.
¿Sientes que la IA está fuera de control? Gobierna, protege y controla cada solicitud con Fastly
Escala tu IA de forma segura. Fastly for AI ofrece a los líderes empresariales visibilidad completa del uso de modelos, controles de costos en tiempo real y protección contra amenazas en el edge
Preventing Automated Security Decisions from Impacting Critical Events
Learn how Fastly DDoS Protection's new Challenge action prevents false positives and keeps legitimate traffic flowing during critical events.
¿Qué es Style Smuggler (CVE-2026-75650)?
CVE-2026-75650 (StyleSmuggler) es una vulnerabilidad SSTI crítica que se está explotando activamente en plataformas de e-commerce. Descubre en qué consiste y cómo los clientes de Fastly pueden mantenerse protegidos.
The New DDoS Playbook: Lessons from Khan Academy, Yottaa, and Magnolia
Khan Academy, Yottaa, and Magnolia stop DDoS attacks with automation that reacts faster than any team could. See how Fastly protects them at scale.
Building Fastly Log Analytics Tools: An Open-Source Approach to Deeper Insights
Gain deeper insights with Fastly Log Analytics. Build an open-source, self-hosted dashboard to own your data, reduce vendor costs, and troubleshoot instantly.
Preserving Analytics Attribution During Bot Challenges: A Fastly VCL & NGWAF Deep Dive
Learn how to preserve Google Analytics attribution during bot challenges. Discover how to use Fastly's NGWAF and VCL to maintain data accuracy while securing your site.
Why SaaS and PaaS Infrastructure Leaders Are Facing 22% More Unwanted Bots
Bot traffic is hammering SaaS and PaaS platforms. Watch Fastly’s on-demand webcast to learn how to adaptively mitigate bot risks, protect your origin, and maintain platform uptime.
The Future of SaaS/PaaS: Every Bot Wants a Bite
Fastly data reveals bots now outnumber humans on high-tech websites, with AI crawlers driving new security, API, and IP protection challenges.
Inside Fastly’s 2026 Internship Program: Projects, Impact & Culture
Go behind the scenes of Fastly’s 2026 Internship Program. See how our intern cohort tackled real-world engineering projects and made a lasting impact.
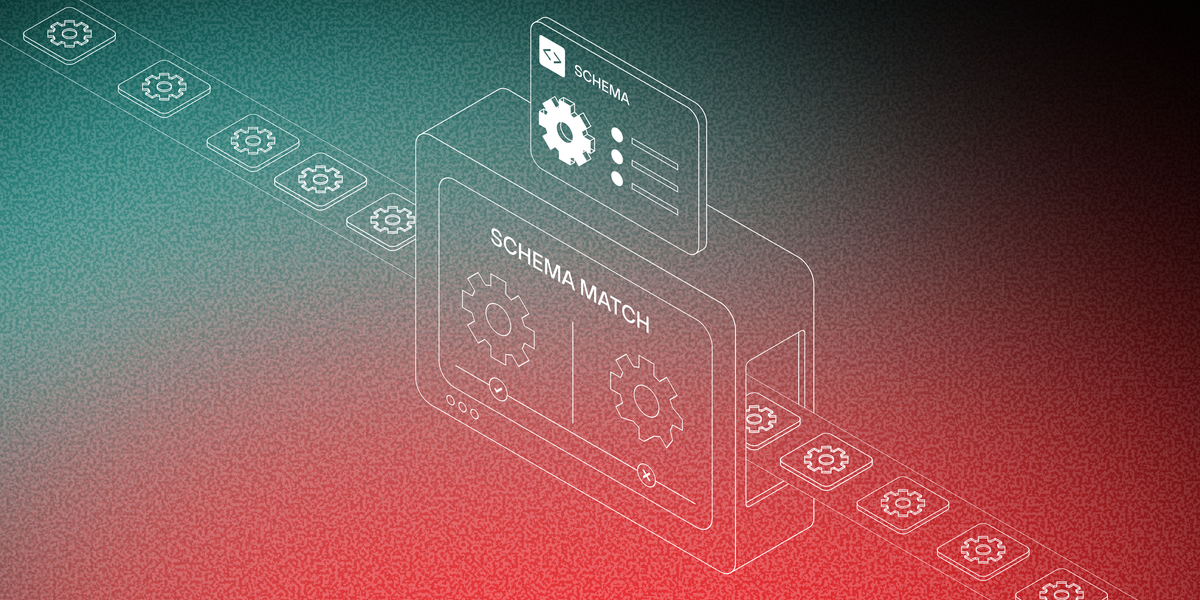
Level Up Your Security with Fastly API Enforcement
Take control of your API landscape with Fastly API Security. Discover, monitor, and enforce schema compliance at the edge to stop threats and secure your apps.

Terraform Your Fastly Config in a few Commands
Import your complete Fastly setup into Terraform in minutes. No rewrites, no downtime, just your existing infrastructure, now as code.
Online Sports’ Shadow Audience
Piracy, bots, and AI-driven attacks shadowed the 2026 World Cup. Here's what the traffic data reveals — and what it means for infrastructure.
What is CVE-2026-66066? Protecting Your Rails App from Active Storage RCE
Learn about CVE-2026-66066: An arbitrary file read vulnerability in Rails Active Storage. Understand the risks and protect your environment with our virtual patch.
What Modern Fintechs Actually Need from Their Security Stack
Ditch fragmented tools and manual tuning. See how high-performing fintechs use edge security to protect payments, APIs, and user trust.