

Ottieni tutto ciò di cui hai bisogno da una CDN moderna: dalla scalabilità senza sforzi alla sicurezza integrata, dal controllo programmabile alla visibilità completa.




Defense Without Detours: Introducing Fastly Network Protect
Discover Fastly Network Protect: scalable, hardwareless Layer 3 and 4 DDoS defense with unmatched global capacity, inline protection, and zero detours.


When a network-layer attack hits, protecting your infrastructure shouldn't mean sacrificing performance, waiting for mitigation to activate, or adding another fleet of hardware to manage.
Yet these are the tradeoffs many organizations face when protecting the networks behind their most critical services. Traditional mitigation architectures can divert traffic through centralized scrubbing centers. On-premises appliances introduce additional infrastructure to deploy and maintain. And when protection isn't always on, the time it takes to activate mitigation can leave critical infrastructure exposed.
What if network protection didn't require a detour?
For more than 15 years, Fastly has helped deliver the internet's biggest moments, and now, today, we're extending that proven global network to protect the infrastructure behind the internet, too.
Meet Network Protect
Network Protect provides Defense without detours, meaning it’s backed by the same capacity and capabilities of our entire global network but built to defend against network attacks (Layers 3 and 4), while eliminating the accepted tradeoffs of legacy solutions. Look to Network Protect to provide your origin infrastructure with unparalleled resiliency, inline protection, and hardwareless defense.
Unparalleled resiliency
The scale of Fastly's global network is now available to help protect your infrastructure.
Fastly operates 622 Tbps of total network capacity**, nearly 20 times the size of the largest recorded DDoS attack. That global scale provides the foundation for resilient network protection.
Network Protect helps absorb and filter unwanted traffic before it reaches your infrastructure, helping keep critical services available when attacks threaten to overwhelm your network.
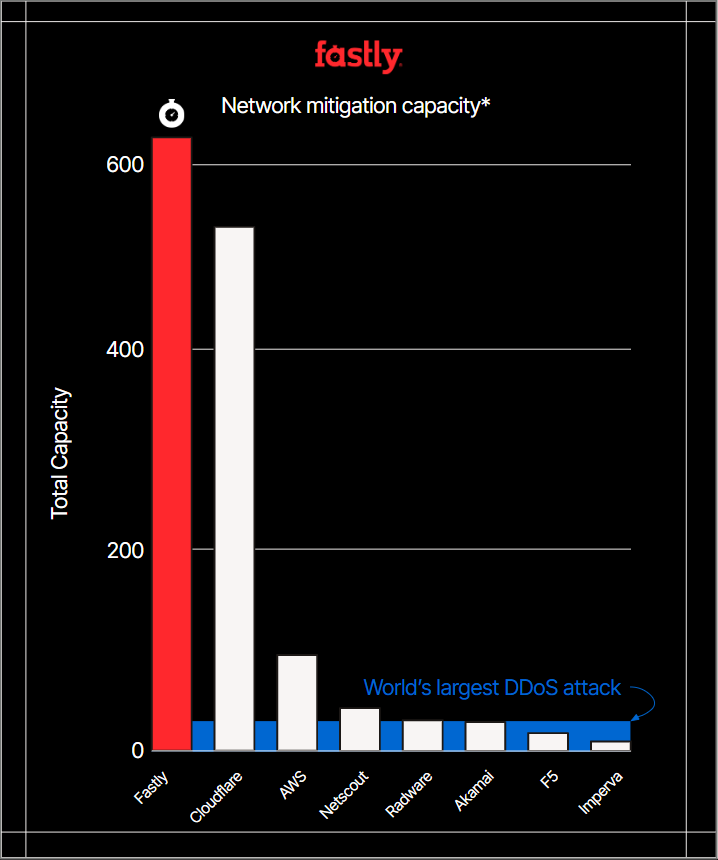
* Capacity represents Fastly’s total global network capacity as of June 30, 2026 versus total or dedicated DDoS mitigation capacity publicly reported by other providers. Cloudflare Network Capacity of 534 Tbps as of October 2, 2026; AWS Mitigation Capacity of 100+ Tbps as of October 2, 2026; Netscout Mitigation Capacity of 33 Tbps as of October 2, 2026; Radware Mitigation Capacity of 30 Tbps as of October 2, 2026; Akamai Dedicated Defense Capacity of 20+ Tbps as of October 2, 2026; F5 Capacity Available for Attack Mitigation of 17 Tbps as of May 2026; Imperva Global Scrubbing Capacity of 13 Tbps as of October 2, 2026. Largest network DDoS attack on record as of November, 2025.
Inline protection
Protection shouldn't come at the cost of performance.
Traditional mitigation architectures can route traffic through centralized scrubbing centers or a subset of a provider's network for inspection. Depending on the architecture, these additional routing steps can increase latency for legitimate traffic.
Network Protect brings protection to Fastly's points of presence (POPs), processing traffic at the edge rather than relying on a distant, centralized scrubbing facility. The nearest applicable POP processes traffic, and permitted traffic is delivered to your network over a Generic Routing Encapsulation (GRE) tunnel.
This architecture supports always-on protection without requiring traffic to detour through a separate scrubbing-center infrastructure. By integrating network traffic filtering into Fastly's global network, Network Protect helps organizations protect their infrastructure while minimizing unnecessary routing complexity.
Hardwareless defense
Protecting your network shouldn't require another fleet of hardware to manage.
On-premises mitigation appliances can provide local control, but they also introduce procurement, capacity planning, maintenance, and replacement costs. Hardware capacity can become a constraint as traffic volumes and attack demands change, while the infrastructure itself requires ongoing operational attention.
Network Protect is software-defined and delivered through Fastly's global network, helping organizations reduce their reliance on dedicated mitigation hardware and the operational burden that comes with it.
Instead of deploying and maintaining another layer of physical mitigation infrastructure, organizations can build on Fastly's network to scale their defenses with less hardware complexity.
How Fastly Network Protect works now
Once onboarded by Fastly’s team of experts, Network Protect provides always-on defense in three simple steps:
Fastly announces your IP prefixes via BGP, pulling all traffic destined for your network through Network Protect
Traffic is screened against your network firewall rules blocking or allowing traffic based based your policies incorporating any combination of IP protocol, source and destination port, or source and destination address
Clean traffic travels directly to your network over GRE tunnel.
Where Network Protect is Going Next
Today's launch is the beginning of a broader vision for Network Protect and network security at Fastly.
Network Protect launches with rule-based network traffic filtering delivered through Fastly's global network. We're also developing enhancements to Fastly's Adaptive Threat Engine, tailored to network-layer traffic and telemetry, with the goal of bringing more automated mitigation of volumetric attacks to the platform.
These future capabilities will build on the foundation available today, advancing our vision of network protection that combines global scale with increasingly intelligent, software-defined defense.
Ready to Get Started?
The infrastructure you deploy to protect your business shouldn't become another bottleneck.
Defense without detours should be the default.
Fastly Network Protect is available now. Talk to an expert to learn how it can help protect your network.
** as of June 30, 2026